AI Agent Compliance Monitoring
Agentic AI presents a new compliance challenge. AI agents — including coding assistants like Claude Code and GitHub Copilot — can read sensitive files, execute commands, access credentials, and process confidential data, all without leaving a trail in traditional audit systems. EMET closes this gap by providing a detailed, cryptographically signed audit trail of AI agent activity that supports compliance evidence collection. Every event is cryptographically signed at the sensor and verified on receipt, providing tamper-evident audit trails as part of a defense-in-depth integrity design.
EMET answers the questions auditors will ask:
- What did the AI read? Every
Readtool invocation, with file paths - What commands did the AI execute? Every
Bashtool invocation, with command strings - What files did the AI create or modify? Every
WriteandEdittool invocation - When did these activities occur? Nanosecond-precision timestamps
- Who requested them? Session and sensor correlation
Supported compliance frameworks:
| Framework | Coverage Areas |
|---|---|
| SOC 2 Type II | Logical access controls, change management, monitoring, incident response |
| HIPAA | PHI access monitoring, audit controls, transmission security, integrity |
| GDPR | Right to erasure, data retention, data portability, privacy by design |
| ISO 27001 | Access control, logging, monitoring, incident response |
Core compliance capabilities:
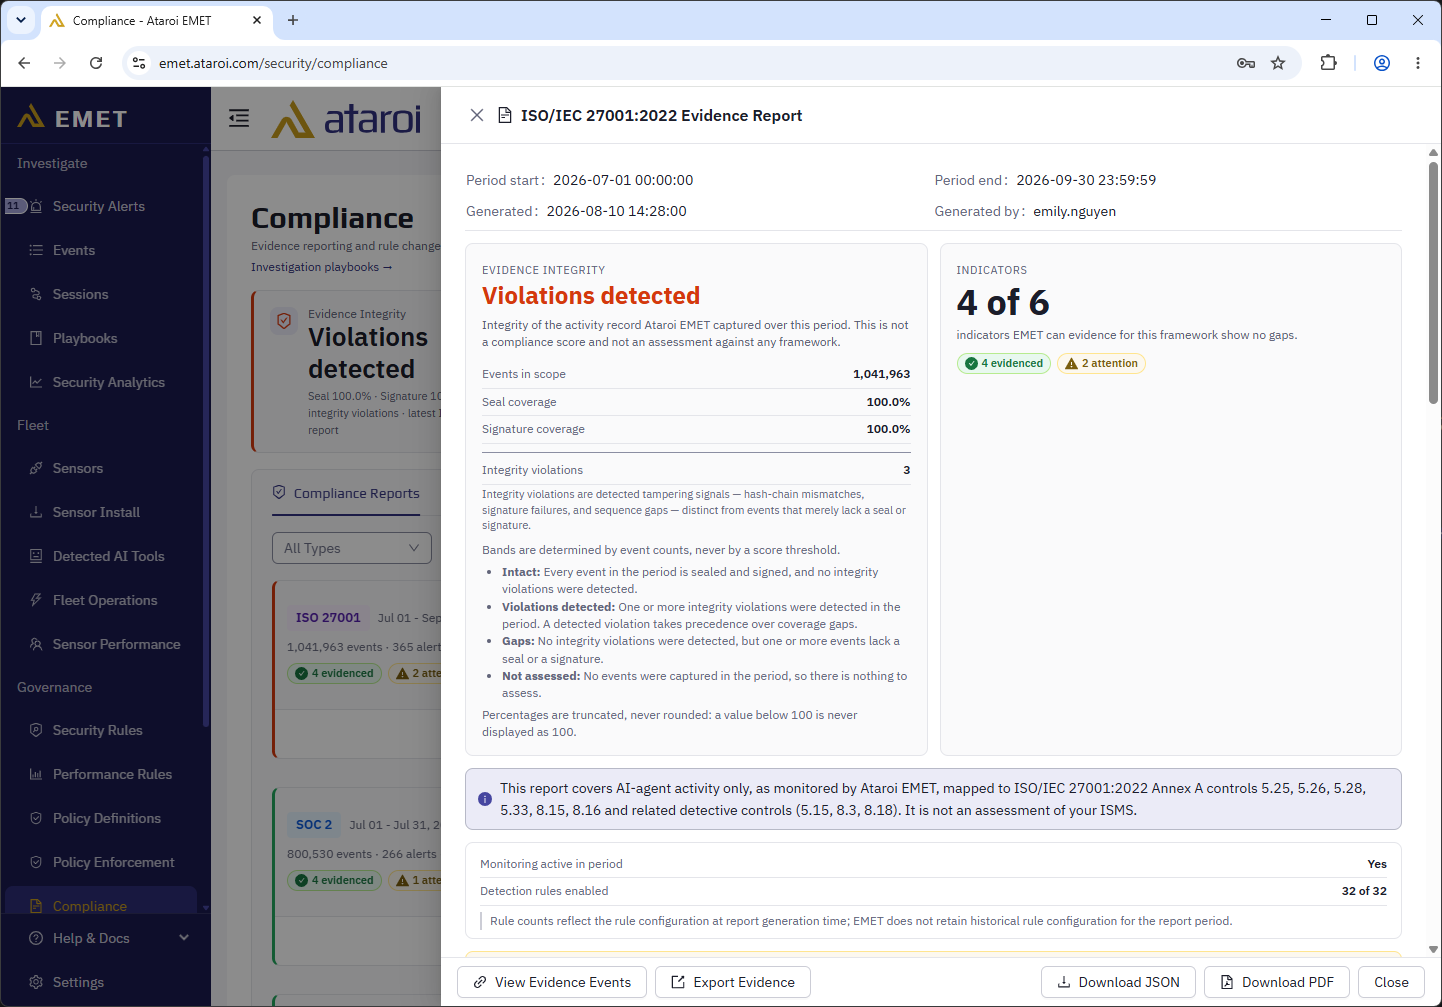
- Signed audit trail — Cryptographic signing at the sensor with server-side verification provides tamper-evident audit trails
- Data export — CSV and JSON exports from Events, Sessions, Security Alerts, and Performance Alerts
- Built-in security rules — Automatic detection of credential access, data exfiltration, privilege escalation, and more
- Role-based access control — Five roles (Viewer, Analyst, Security Manager, Tenant Admin, Platform Admin) enforced on every API endpoint
- Data retention — 30 days on Starter, 90 days on Pro, up to 365 days on Enterprise; configurable on Pro and Enterprise
- GDPR Article 17 — Full tenant data purge with survivor audit record
EMET's compliance capabilities work alongside its SIEM integration to feed AI activity data into your existing security operations workflows. For an overview of EMET's monitoring architecture and core capabilities, see What is Ataroi EMET?.
:::info Available on Pro and Enterprise Plans
Detailed compliance documentation, including framework-specific control mappings, evidence collection guides, audit report templates, and recommended controls checklists, is available to EMET Pro and Enterprise customers within the dashboard.
Sign in to your EMET dashboard →
:::