GDPR Compliance for AI Agents
The General Data Protection Regulation (GDPR) applies when EU residents' personal data may appear in AI agent activity. EMET is designed with privacy-by-design principles built in from the ground up, supporting the key GDPR rights and obligations relevant to AI activity monitoring.
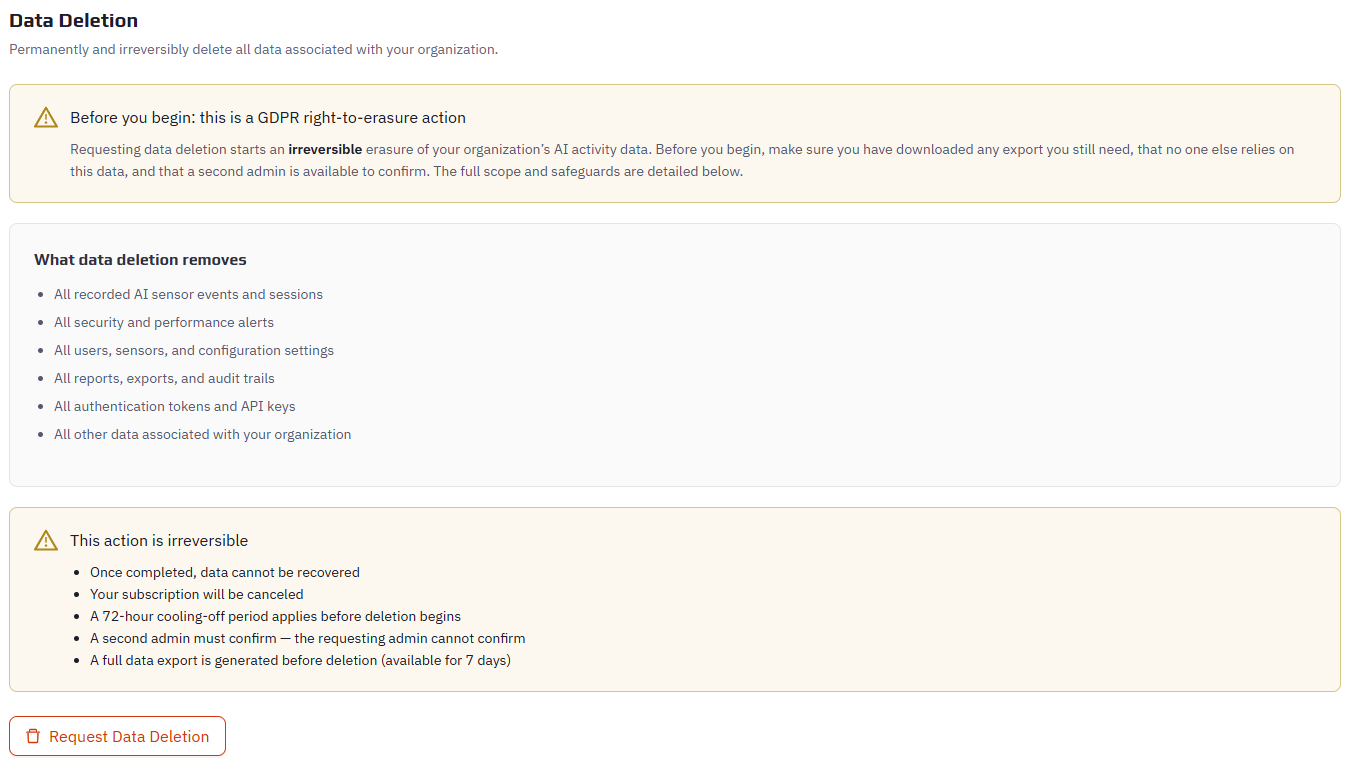
EMET supports GDPR rights:
- Article 15 — Right of Access — Export user activity from the Events page filtered by sensor, in CSV or JSON format
- Article 17 — Right to Erasure — Full tenant data purge across the entire database with irreversible deletion, cooling-off period, and survivor audit record; per-sensor identity removal with event data expiring via retention policy
- Article 20 — Data Portability — Machine-readable JSON and human-readable CSV exports
- Article 25 — Privacy by Design — Data minimization through configurable capture payloads, purpose limitation to AI monitoring only, storage limitation with automatic retention-based deletion, and security through TLS 1.3, RBAC, and cryptographic signing
Additional GDPR capabilities:
- Data retention (30 days Starter / 90 days Pro / up to 365 days on Enterprise) with nightly automatic deletion, configurable on Pro and Enterprise
- Personal data categories tracked: hostnames, usernames, IP addresses, user prompts, file contents, command outputs
- Self-hosted deployment option for EU data residency requirements
- Data Processing Agreement (DPA) available for cloud SaaS deployments
For a broader view of EMET's compliance support, see the Compliance Overview. EMET also supports SOC 2, HIPAA, and ISO 27001 evidence collection.
:::info Available on Pro and Enterprise Plans
Detailed GDPR compliance documentation, including data processing inventories, DPIA guidance, DPA request process, transfer mechanism details, and a complete GDPR deployment checklist, is available to EMET Pro and Enterprise customers within the dashboard.
Sign in to your EMET dashboard →
:::